Compliance-as-a-Service: Moving from Annual Audits to Continuous Compliance
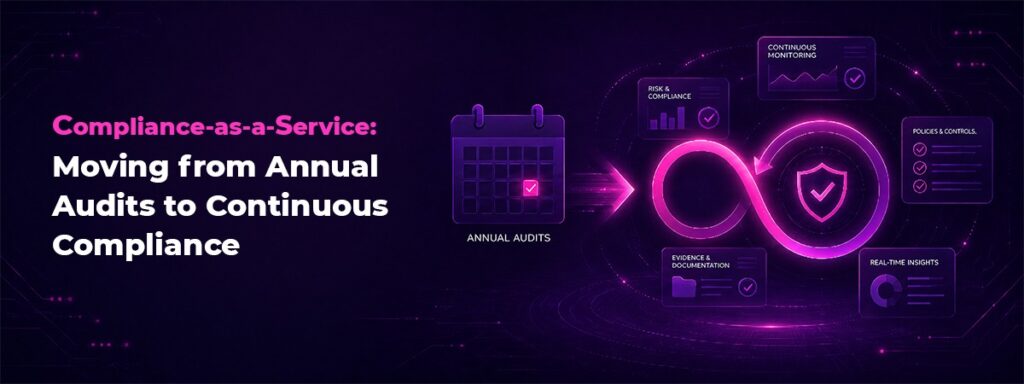
For many organisations, compliance still follows a familiar cycle. Then the audit is completed, and compliance activity gradually slows down until the next assessment. But today’s regulatory and cybersecurity environment is making this approach increasingly difficult to sustain. Regulations change. Technology environments change. Vendors change. Business processes change. And risks change continuously. This is driving […]